Building incident playbooks for machine identity breaches
Pull up your SOC’s compromised account playbook and read through the first 15 minutes. Most SOCs […]
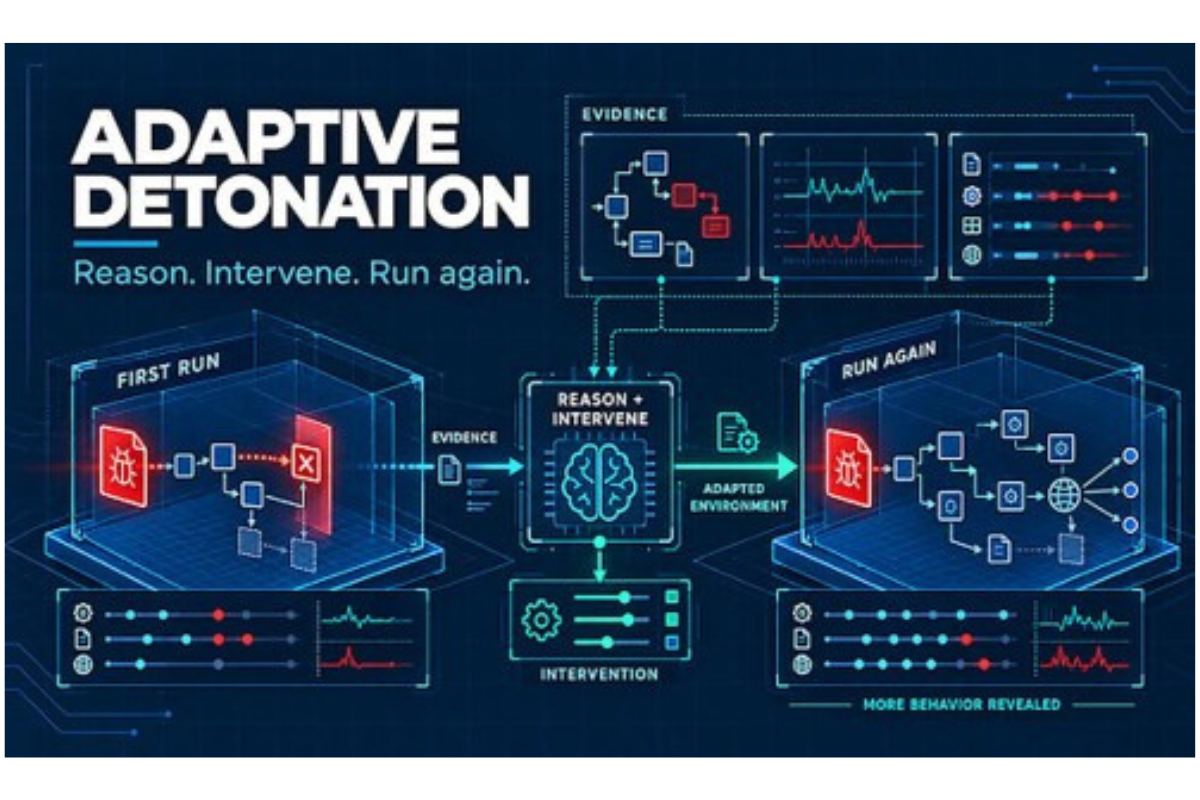
The Sandbox Fights Back: Joe Security Launches Adaptive Detonation
AI agents help Joe Sandbox uncover malicious behavior concealed by evasion techniques and unmet execution conditions. […]
Attackers turned OpsShield’s trusted update channel into a supply-chain attack
The kinks in the software supply chain are once again being exposed, with attackers now targeting […]
Fake software installers are turning your PCs into profit centers for hackers
Users looking for cracked commercial software, free games, plugins, and unofficial utilities could be signing up […]
CrowdStrike launches AI kill switch to shut down rogue agents
With a notable rise in autonomous AI agents veering off-script inside corporate networks, CrowdStrike has launched […]
CrowdStrike to acquire Fiddler, Dreadnode to extend AI security across agent lifecycle
CrowdStrike plans to acquire AI security companies Fiddler AI and Dreadnode in separate deals that will […]
CrowdStrike’s AI SOC vision evolves as agentic uncertainty adds new twist
“The software we use has become an actor,” declared CrowdStrike President Michael Sentonas in his address […]
Barracuda’s security appliances have a security problem of their own
Barracuda, which offers a wide variety of cybersecurity devices, has been bitten by a bug itself. […]
Node-RED authentication hole being exploited in the wild
Months after Siemens released fixes for an authentication hole in flow-based programming tool Node-RED, it remains […]
Critical Langflow flaws enable authentication bypass and RCE
IBM patched critical vulnerabilities in Langflow, an open-source framework for building AI agents, LLM-powered workflows, and […]