
Deception Technology Implementation Best Practices: A Practical Guide for Enterprise Security Teams
Key Takeaways Define deception goals around detection speed, threat intelligence, and team capacity before choosing a […]
From JADEPUFFER to Multi-Agent Intrusions: The Next Wave of Autonomous Attacks
Key Takeaways JADEPUFFER proved one AI agent could run a full attack chain without a human […]
Why Internal Attack Surface Management Needs Continuous Network Visibility
Key Takeaways Static inventories confirm asset existence, but continuous visibility reveals real-time security risks, active behavior, […]
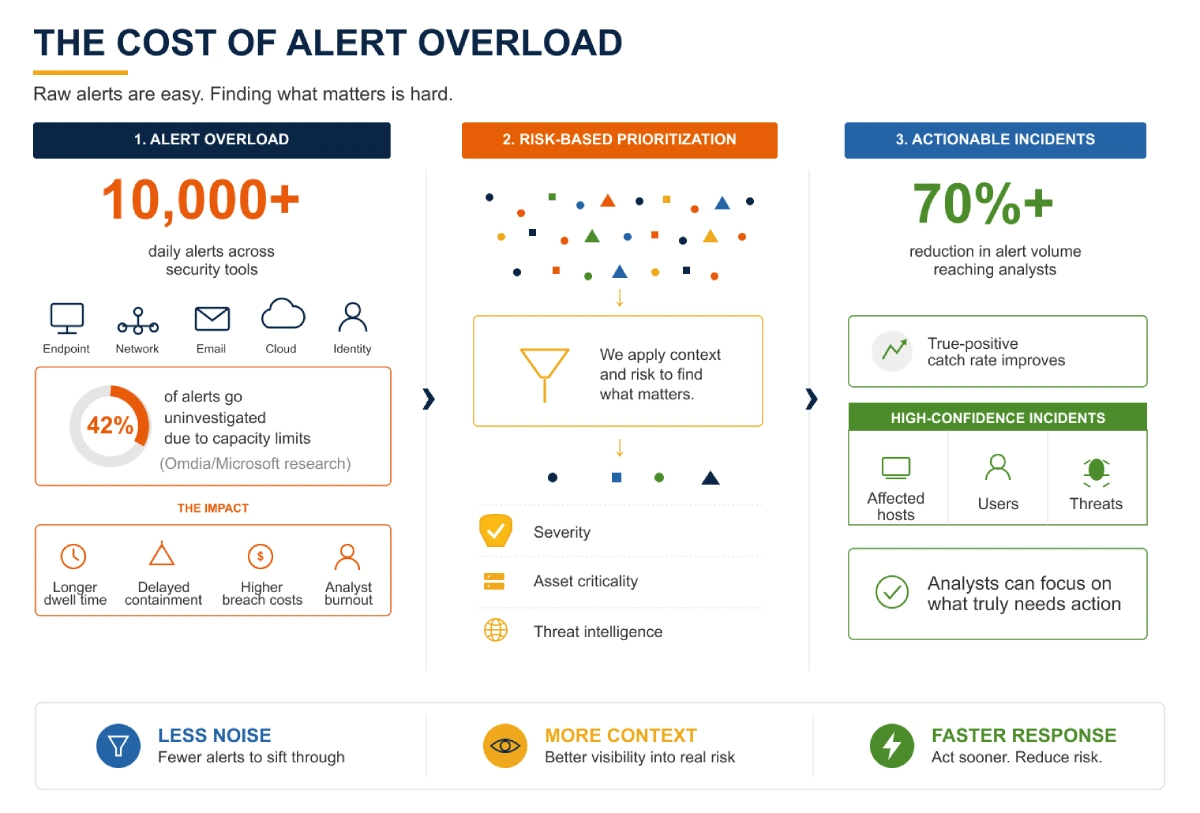
Alert Prioritization in Security Operations: How Fidelis Helps Focus on the Threats That Matter
Key Takeaways Enterprise SOCs handle thousands to tens of thousands of alerts a day, and up […]
How to Test a DDoS Incident Response Playbook with Tabletop Exercises
Key Takeaways Use tabletop exercises to test DDoS response plans without generating attack traffic. Build scenarios […]
Fed Warns AI Can Chain Cyber Exploits as Its Own Security Governance Falls Short
The Fed warns frontier AI can automate exploit chains at machine speed while its own cybersecurity […]
Fed warnt: KI kann Cyberangriffe zu Exploit-Ketten verknüpfen, während die eigene Sicherheits-Governance Schwächen aufweist
Die Fed warnt, dass Frontier-KI Exploit-Ketten mit Maschinengeschwindigkeit automatisieren kann, während die Schwächen ihrer eigenen Cybersicherheits-Governance […]
La Fed avertit que l’IA peut enchaîner les exploits informatiques, tandis que sa propre gouvernance de la sécurité montre ses limites
La Fed avertit que l’IA de pointe peut automatiser des chaînes d’exploitation à la vitesse de […]
OpenAI Astra vs. CrowdStrike SafeMind: How Two AI Cyber Defense Strategies Are Converging
OpenAI Astra and CrowdStrike SafeMind approach AI cyber defense differently, but their new partnership points toward […]
OpenAI Astra vs. CrowdStrike SafeMind: How Two AI Cyber Defense Strategies Are Converging
OpenAI Astra und CrowdStrike SafeMind verfolgen unterschiedliche Ansätze für KI-Cyberabwehr, doch ihre neue Partnerschaft deutet auf […]