How DFIR Helps Determine Root Cause, Scope, and Impact After a Breach
Key Takeaways Digital forensics incident response determines root cause by tracing activity backward from the first […]
OpenAI Overhauls AI Safety Controls as Models Reach ‘Critical’ Cyber Threshold
OpenAI is tightening security controls and rethinking its Preparedness Framework as advanced AI models create new […]
How Fidelis Enables High-Confidence Threat Detection
Key Takeaways Correlates endpoint, network, cloud, identity, and behavioral telemetry to deliver high-confidence threat detection with […]
What to Expect from an EDR Rollout: Deployment Considerations, Costs, and ROI
Key Takeaways Ensure a successful EDR rollout by creating endpoint inventory, preparing the infrastructure, configuring policies, […]
China’s Z.ai Claims GLM-5.3 Rivals Top US Models in Coding, Cybersecurity
Z.ai says GLM-5.3 approaches leading U.S. models on coding and cybersecurity benchmarks while delaying its open-weight […]

XDR Deployment Considerations: Data Privacy, Compliance, and Automated Incident Response
Key Takeaways Understand the fundamental XDR deployment considerations and how to balance privacy, compliance, and automated […]
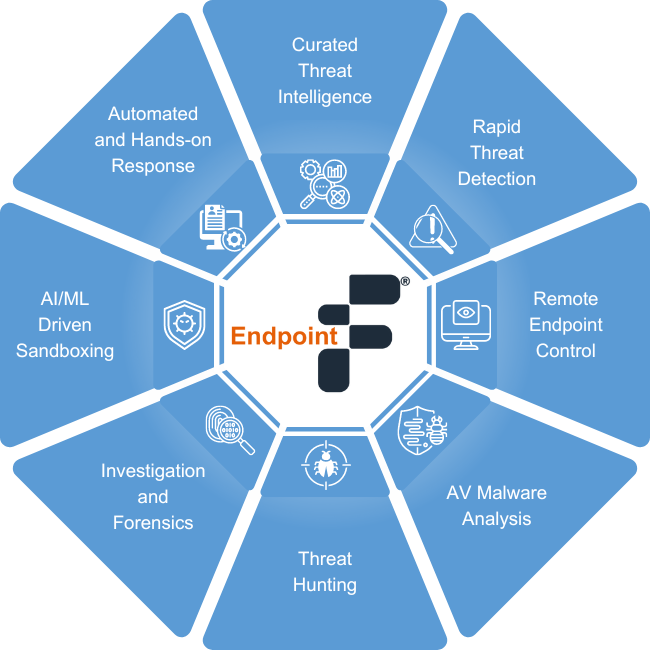
How Fidelis Endpoint Strengthens Enterprise Malware Protection
Key Takeaways Explains why traditional antivirus solutions are no longer sufficient against modern malware. Discusses how […]
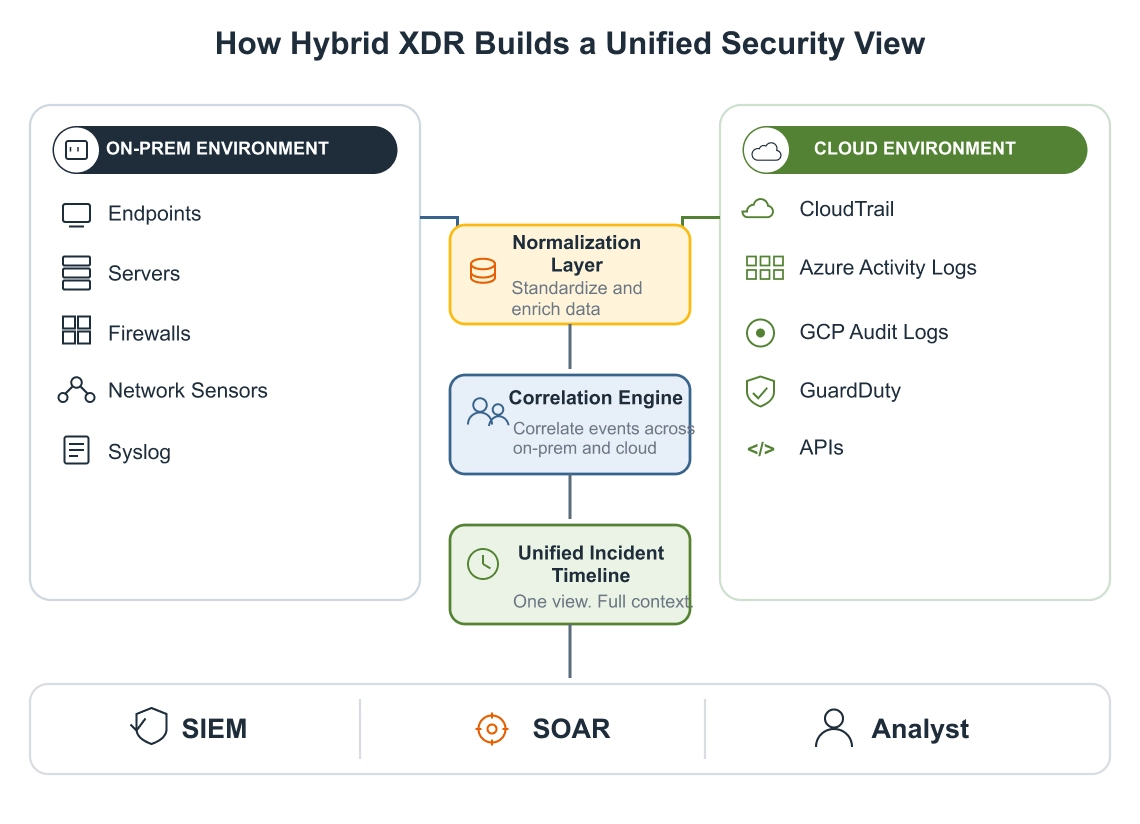
How to Deploy XDR Across On-Prem and Cloud Environments: A Step-by-Step Strategy
Key Takeaways Inventory from authoritative sources (cloud asset APIs, Terraform state), not a spreadsheet someone updates […]
How Behavioral EDR Improves Malware Hunting Accuracy
Key Takeaways Behavioral EDR improves malware hunting accuracy by analyzing endpoint behavior instead of relying solely […]
Malware Traffic Analysis for EDR Teams: How to Connect Endpoint Events to Network Behavior
Key Takeaways Endpoint alerts are not enough and should be correlated with network traffic to add […]