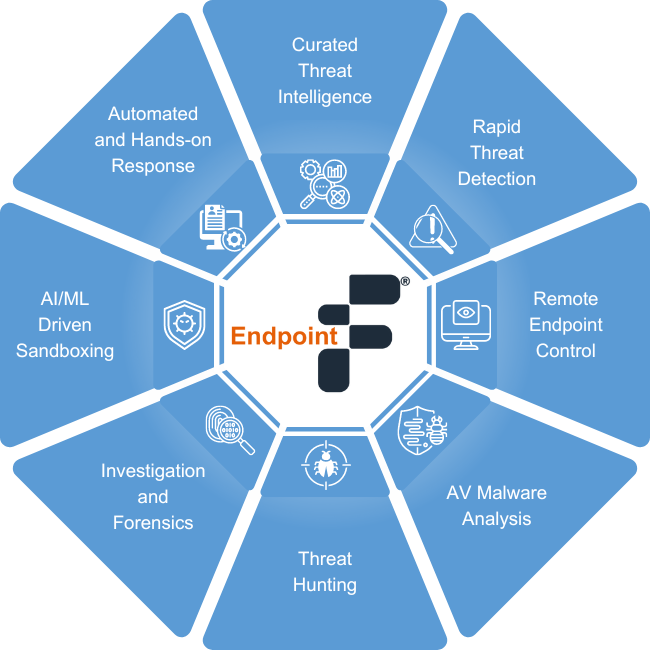
How Fidelis Endpoint Strengthens Enterprise Malware Protection
Key Takeaways Explains why traditional antivirus solutions are no longer sufficient against modern malware. Discusses how […]
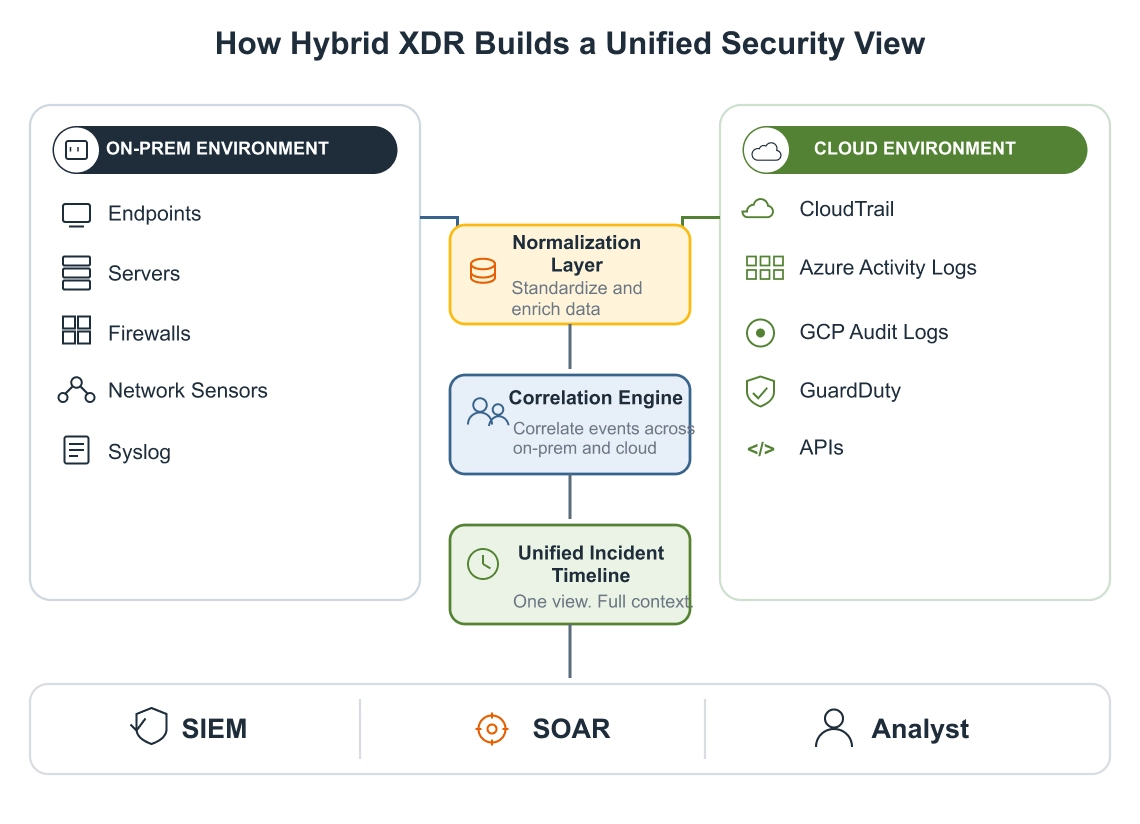
How to Deploy XDR Across On-Prem and Cloud Environments: A Step-by-Step Strategy
Key Takeaways Inventory from authoritative sources (cloud asset APIs, Terraform state), not a spreadsheet someone updates […]
How Behavioral EDR Improves Malware Hunting Accuracy
Key Takeaways Behavioral EDR improves malware hunting accuracy by analyzing endpoint behavior instead of relying solely […]
Malware Traffic Analysis for EDR Teams: How to Connect Endpoint Events to Network Behavior
Key Takeaways Endpoint alerts are not enough and should be correlated with network traffic to add […]
How Fidelis Container Secure Helps Reduce Container Security Vulnerabilities Across Docker and Kubernetes
Key Takeaways Runtime is the primary attack surface; pre-deployment scans miss active threats after deployment Misconfigurations, […]
Blue Cloud Softech Lands $150 Million Deal to Build Malaysia AI Infrastructure
Blue Cloud Softech’s US subsidiary has signed a minimum $150 million, 18-month AI infrastructure deal in […]
How Fidelis Network Behavior Analysis Detects Advanced Threat Activity
Key Takeaways Network behavior analysis detects advanced threats by modeling normal activity first. Fidelis’ Deep Session […]
Cloud Incident Response: How to Detect, Contain, and Recover from Cloud Threats
Key Takeaways Cloud incident response requires identity-first detection, cloud-native visibility, and API-driven containment rather than traditional […]

Incident Response Playbook: How to Build Actionable Workflows Before an Attack Happens
Key Takeaways An effective incident response playbook defines clear decision points, ownership, and default actions so […]

How Fidelis XDR Supports AI Risk Management Across Network, Endpoint, and Deception Layers
AI systems are infrastructure now, and adversaries treat them that way, probing inference APIs, poisoning training […]